THE JUNEI HOTEL KYOTO ザ・ジュネイホテル - 京都御所西・東山のホテル | 新着情報


新着情報
- HOME
- 新着情報
 空室検索

ベストレート保証 公式サイトからのご予約が最もお得です
-
2026.10.26 お知らせ
Notice Regarding Information Leakage
26 October 2026
THE JUNEI HOTEL Kyoto
THE JUNEI HOTEL Kyoto Gosho Nishi
We have learned that WASIMIL, a hotel management system provided by an external company (AZOO Inc.) and used by our hotels for reservations and guest management, was subject to unauthorized access by a third party, and that the personal information of guests who have stayed with us or hold a reservation with us may have been exposed as a result.
We sincerely apologize for the great concern and inconvenience this has caused our guests.
In connection with this incident, we have confirmed cases in which guests received suspicious messages (via WhatsApp, email, etc.) impersonating our hotel and asking them to enter credit card details. Please read the warning below first, and do not open links in suspicious messages or enter your card details.
The facts confirmed to date and the actions we are taking are set out below.
Messages that misuse leaked reservation details (name, stay dates, amount, etc.) and impersonate our hotel to request credit card details or payment are being sent via WhatsApp and email. These messages were not sent by our hotel or by the system provider. They are fraud committed by a third party.
What our hotel does not do
• We never ask you to pay or “re-confirm” by a deadline on the grounds that “verification is required to keep your reservation” or that “your reservation is under review.”
• We never send advance payment links to guests who have booked with payment at the property.
Features of the fraudulent messages confirmed so far
• WhatsApp messages from overseas phone numbers (e.g. +44)
• Your actual reservation details (name, stay dates, amount) are correctly stated
• Links to domains that are not ours (juneihotel.com), such as “gueststaypending.com”
• Requests to enter card details under the pretext of “reservation confirmation” or “review”
What we ask of you
• Do not open links in suspicious messages, and do not enter card details or personal information.
• If you are unsure whether a message about your reservation is genuine, contact our official contact details (at the end of this page) directly, not the contact details in the message.
• If you have already entered your card details, contact your card issuer immediately to block the card and report the fraudulent transactions. We also recommend that you consult the police (in Japan: Cybercrime Consultation Desk #9110; overseas: the police in your country of residence).
• If you receive a suspicious message, please let us know with a screenshot. We will use it for our investigation and for requesting the takedown of fraudulent websites.
Please note that credit card information is not included in the information that may have been leaked (the system does not store card information). Card fraud has occurred where guests entered their card details on a fraudulent website.
1. Summary of the incident
WASIMIL, a hotel management system provided by AZOO Inc. (Tokyo), to which our hotels outsource the management of guest information, was subject to unauthorized access by a third party exploiting a vulnerability in its externally exposed functions. Guest information registered in the system may have been viewed and obtained.
From around 18:00 on 13 October 2026 to the early hours of 17 October 2026 (Japan time). Unauthorized access and data downloads from three IP addresses were confirmed during this period
Affected system
WASIMIL hotel system provided by AZOO Inc. (externally exposed functions such as the booking engine and guest portal)
Detection by the system provider
Initial report received on 17 October 2026; leak confirmed on 19 October 2026
Report to our hotel
Initial notification from the system provider on 20th October 2026; preliminary incident report received on 22 October 2026
Remediation of the vulnerability
Completed on 19 October 2026. No further unauthorized access has been detected since
According to the system provider, due to the log retention period, it is not possible to confirm whether any access occurred before around 16 September 2026. We have requested that the provider report on this point as part of its investigation findings.
2. Information that may have been leaked
Because it is not possible to identify individually which information was actually obtained, in accordance with the rules of Japan’s Personal Information Protection Commission we treat all information that was “accessible” through the unauthorized access as “information that may have been leaked.”
All guests (including the person who made the reservation and accompanying guests) whose information was registered in our hotels’ WASIMIL system on or before 19 October 2026, regardless of the booking channel (our official website, booking sites, telephone, etc.) or the date of booking.
Personal details Name, gender, age, date of birth, nationality, language
Contact details Email address, telephone number, address, emergency contact
Stay details Reservation number, stay dates, room, number of guests, accompanying guests, amount, payment status, notes such as requests
Other Information entered at online check-in (allergies, special requirements, etc.)
• Credit card information (card number, expiry date, security code): not stored in the system.
• Passport numbers and passport images: our hotels do not register passport numbers in the system; the number of guests affected is zero.
According to the system provider’s investigation, it has been confirmed that, for at least some guests, the name, email address, telephone number, property name, stay dates and reservation amount were actually obtained.
3. Cause
According to the system provider’s investigation, a third party exploited a vulnerability in the externally exposed functions of the WASIMIL hotel system (booking engine, guest portal, etc.) to view and obtain guest information that should not have been accessible. Our hotels’ internal systems and accounts were not compromised.
The cause has been identified and the vulnerability was remediated on 19 October 2026.
4. Current response
Actions on the system side (by the system provider)
• On 19 October 2026, remediation of the vulnerability was completed and the access route used in the attack was disabled
• Database connection credentials were reissued and monitoring was strengthened
• As of 22 October 2026, it has been confirmed that there has been no access from the IP addresses used in the attack, no use of the disabled access route, and no large-scale data download
Actions by our hotels
• In place of individual notification to each guest, this public notice and the dedicated contact point below serve as notification of this incident
• We have requested the takedown of the fraudulent websites that have been identified and have filed a report with the police
• We will further strengthen the security of the systems that handle guest information and will continue to apply two-factor authentication
Reporting to the authorities
A preliminary report was submitted to the Personal Information Protection Commission of Japan, the competent authority in Japan, by AZOO Inc. as of 20 October 2026. Once the investigation is complete, a final report will be submitted jointly in the names of our hotels and AZOO Inc.
5. Measures to prevent recurrence
• The authentication method for externally exposed functions has been changed to short-lived tokens scoped to each property (implemented)
• Introduction of a mechanism that limits access scope for each guest
• Retirement of legacy connection routes and reissue of connection credentials
• IP address restrictions on access to the administration console and migration to passkey authentication
• We will require the system provider to conduct a third-party vulnerability assessment and report the results, and we will review its security management status on a regular basis
• We will review the security measures of all external service providers used by our hotels
• We will strengthen information security training for our staff
6. Contact for inquiries about this matter
For questions about this incident, to report a suspicious message you have received, or to check whether your information is affected, please contact us at the details below.
THE JUNEI HOTEL Kyoto
Email: info.kyoto@juneihotel.com / Tel: +81-75-525-0050
THE JUNEI HOTEL Kyoto Imperial Palace West
Email: info@juneihotel.com / Tel: +81-75-415-7774
Once again, we deeply apologize for the great concern and inconvenience this incident has caused our guests. We regard the protection of our guests’ personal information as our highest priority and will do everything in our power to prevent a recurrence. -
2026.10.26 お知らせ
不正アクセスによるお客様の個人情報漏洩に関するお詫びとご報告及びご注意喚起
2026年10月26日
THE JUNEI HOTEL 京都
THE JUNEI HOTEL 京都 御所西
このたび、当館がお預かりしておりますお客様の個人情報が、当館の宿泊予約・顧客管理ホテルシステム「WASIMIL」(提供:株式会社AZOO)への第三者による不正アクセスを受け、外部に漏えいしたことが判明いたしました。
お客様には多大なるご迷惑とご心配をおかけしておりますことを、心より深くお詫び申し上げます。
システムの運営は外部の事業者に委託しておりますが、お客様の情報をお預かりしていたのは当館です。本件への対応は、委託先の管理を含めて当館の責任において行ってまいります。
本件に関連して、当館を装い、クレジットカード情報の入力を求める不審なメッセージ(WhatsApp・メール等)がお客様に届いている事例を確認しております。まずは下記のご注意喚起をご確認いただき、不審なメッセージのリンクを開いたり、カード情報を入力したりなさらないようお願い申し上げます。
現時点で判明している事実と当館の対応について、以下のとおりご報告いたします。 漏えいしたご予約情報(お名前・宿泊日・金額等)を悪用し、当館からの連絡を装ってクレジットカード情報の入力や支払いを求めるメッセージが、WhatsAppやメールで届いています。これらは当館およびシステム提供会社が送信したものではなく、第三者による詐欺です。
<当館が行わないこと>
・「予約を維持するために確認が必要」「予約が審査中」といった理由で、期限を区切って支払いや再確認を求めることはありません。
・現地払いでご予約のお客様に、事前決済のリンクをお送りすることはありません。
<確認されている不審なメッセージの特徴>
・海外の電話番号(+44 など)からのWhatsAppメッセージ
・実際のご予約内容(お名前・宿泊日・金額)が正しく記載されている
・「gueststaypending.com」など、当館のドメイン(juneihotel.com)ではないリンク先
・「予約の確認」「審査」と称してカード情報の入力を求める
<お客様へのお願い>
・不審なメッセージのリンクを開かず、カード情報や個人情報を入力しないでください。
・ご予約に関する連絡の真偽が不明な場合は、メッセージ内の連絡先ではなく、当館の公式連絡先(本ページ末尾)まで直接お問い合わせください。
・すでにカード情報を入力してしまった場合は、速やかにカード発行会社へ連絡し、カードの利用停止と不正利用の申告を行ってください。あわせて、警察(日本国内:サイバー犯罪相談窓口 #9110/海外:お住まいの国の警察)へのご相談をお勧めします。
・不審なメッセージを受信された場合は、お手数ですがスクリーンショットを添えて当館までお知らせください。調査および偽サイトの閉鎖要請に活用いたします。
なお、今回漏えいしたおそれのある情報にクレジットカード情報は含まれておりません(当該システムはカード情報を保持していません)。カードの被害は、偽サイトにカード情報を入力した場合に発生しています。
1. 事案の概要 当館は、宿泊者様の情報の管理を株式会社AZOO のホテルシステム「WASIMIL」で行っています。同システムの外部公開機能の脆弱性を突いた第三者の不正アクセスにより、当館の宿泊者様の情報が閲覧・取得されました。
項目 内容 不正アクセスの発生期間 2026年10月13日18時頃〜10月17日未明(日本時間)。この間、3つのIPアドレスからの不正アクセスとデータのダウンロードが確認されています 対象システム 株式会社AZOO提供のホテルシステム「WASIMIL」(予約エンジン・ゲストポータル等の外部公開機能) システム提供会社による認知 2026年10月17日に一報を受け、同月19日に漏えいを確認 当館への報告 2026年10月20日にシステム提供会社より第一報、同月22日に一次報告書を受領 脆弱性の修正 2026年10月19日に完了。以降、新たな不正アクセスは確認されていません
なお、システム提供会社によれば、ログの保存期間の関係から2026年9月16日頃より前のアクセスの有無は確認できないとのことです。当館では、この点も含めて調査結果の報告を求めています。
2. 漏えいした情報 実際に取得された情報を個別に特定することができないため、個人情報保護委員会の規則に基づき、不正アクセスにより「閲覧可能な状態にあった」すべての情報を「漏えいした情報」として扱っています。
システム提供会社の調査によれば、少なくとも一部の宿泊者様について、氏名・メールアドレス・電話番号・施設名・宿泊日程・予約金額が実際に取得されたことが確認されています。
<対象となるお客様>
2026年10月19日以前に当館のWASIMILに登録されていたすべての宿泊者様(ご予約者様・同行者様を含む)。ご予約の経路(当館公式サイト・予約サイト・お電話等)や時期を問いません。
<対象となる情報の項目> 区分 項目 本人情報 氏名、性別、年齢、生年月日、国籍、言語 連絡先 メールアドレス、電話番号、住所、緊急連絡先 宿泊情報 予約番号、宿泊日程、客室、人数、同行者、金額、入金状況、ご要望等のメモ その他 オンラインチェックインでご入力いただいた情報(アレルギー・ご配慮事項等)
<対象外の情報>
・クレジットカード情報(カード番号・有効期限・セキュリティコード):当該システムには保存されていません。
・旅券番号および旅券画像:当館では当該システムに旅券番号を登録しておらず、対象は0名です。
・当館内で保管・管理するお客様の個人情報:今回の不正アクセスは、外部の予約管理システム「WASIMIL」に対して行われたものでございます。当館の社内システムおよび紙媒体にて厳重に保管・管理している情報は本件の対象外であり、これらへの影響は一切ございません。
・公式HPからのご予約頂いたお客様のパスワード、当館従業員のアカウント情報、外部予約サイト等へのログイン情報:上記の各種認証情報につきましても、本件の漏洩対象には含まれておりません。従いまして、お客様におかれまして、直ちにパスワードをご変更いただく等のご対応は不要でございます。
なお、上記は現時点におけるお客様への影響範囲を明確にし、ご確認いただく目的でお知らせするものでございます。漏洩が確認された情報につきましては、その管理責任が当館にあるという事実に変わりもございません。
3. 原因 システム提供会社の調査によれば、ホテルシステム「WASIMIL」の外部公開機能(予約エンジン・ゲストポータル等)に存在した脆弱性を第三者が悪用し、本来アクセスできないはずの宿泊者情報を閲覧・取得したものです。原因となった箇所は特定され、2026年10月19日に修正が完了しています。 当館は、委託先の安全管理状況の確認が十分であったかを含め、当館の管理体制についても検証を行っています。
4. 現在の対応状況 <システム側の対応(システム提供会社によるもの)>
・2026年10月19日、脆弱性の修正を完了し、不正に使用されたアクセス手段を無効化
・データベース接続情報の再発行と監視体制の強化
・2026年10月22日時点で、攻撃に使われたIPアドレスからのアクセス、無効化したアクセス手段の使用、大量のデータダウンロードがいずれもないことを確認
<当館の対応>
・メールアドレスをお預かりしておりますお客様へは本件のご通知を個別にお送りしています。個別のご通知が困難なお客様については、本ページでの公表およびお問い合わせ窓口の設置をもってご通知とさせていただきます。
・確認された偽サイトについては、閉鎖要請および警察への届出を行っています。
・お客様の情報を取り扱うシステムについては、セキュリティ対策をより一層強化するとともに、二段階認証を引き続き実施してまいります。
・被害を申告いただいたお客様には、カード会社への申請に必要な証明書類の発行など、個別に対応しています。
・システム提供会社に対し、第三者による脆弱性診断の実施と結果の報告を要請しました。
・関係当局への報告
日本の関係当局である個人情報保護委員会へは、株式会社AZOOより2026年10月20日時点で速報を提出済みです。当館と株式会社AZOOの連名にて続報を提出いたしました。
5. 再発防止策 <システム提供会社における対策> 外部公開機能の認証方式を、短時間で失効し施設ごとに範囲を限定したトークン方式へ変更(実施済み) 宿泊者ごとにアクセス範囲を限定する仕組みの導入 旧来の接続経路の廃止と接続情報の再発行 管理画面へのアクセスに対するIPアドレス制限、パスキー認証への切り替え <当館における対策> システム提供会社に対し、第三者による脆弱性診断の実施と結果の報告を要請し、定期的な安全管理状況の確認を行います 当館が利用する外部システム全般について、委託先の安全管理措置の点検を実施します スタッフへの情報セキュリティ教育を強化します
6. 本件に関するお問い合わせ窓口 本件に関するご質問、不審なメッセージを受信された場合のご報告、ご自身が対象に含まれるかのご確認は、下記までご連絡ください。
THE JUNEI HOTEL 京都
メール:info.kyoto@juneihotel.com/電話:+81-75-525-0050
THE JUNEI HOTEL 京都 御所西
メール:info@juneihotel.com/電話:075-415-7774
このたびは、お客様に多大なご迷惑とご心配をおかけしておりますことを、重ねて深くお詫び申し上げます。当館は、お客様の個人情報の保護を最優先の課題として、再発防止に全力で取り組んでまいります。
<更新履歴>
2026年10月26日 本お知らせを掲載
2026年10月31日 当館の責任を明確化するため文言を改訂 -
2026.10.11 お知らせ
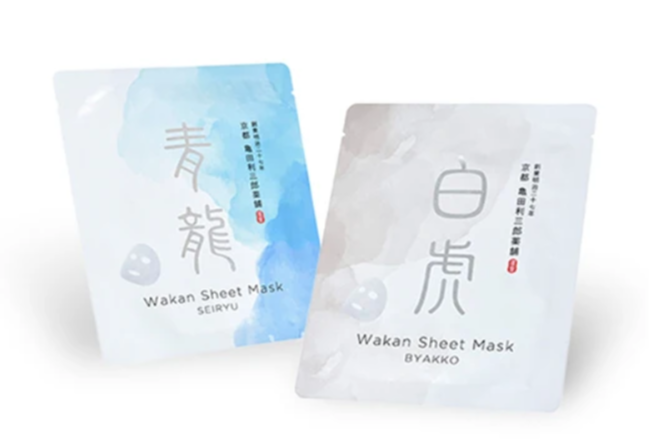
亀田利三郎薬舗の和漢シートマスク付きプランを公式予約にて限定販売!
京都の老舗・亀田利三郎薬舗が手がける「和漢シートマスク」を公式サイト限定のプラン特典としてご用意致しました。
厳選された和漢美容成分と、肌に密着するバイオセルロースシートで、うるおいに満ちた肌へ。
日本の伝統と知恵を感じる、特別なスキンケア体験をお楽しみください。
シートマスク「青龍」
・こんな方におすすめ
お肌のキメを整え、すこやかで澄んだ印象を目指したい方。
スキンケアタイムに、上品なローズの香りでゆったりとリラックスしたい方。
シートマスク「白虎」
・こんな方におすすめ
お肌に明るくうるおいのある印象を求める方。 スキンケアタイムに、すがすがしいローズマリーの香りでリフレッシュしたい方。
シートマスク「朱雀」
・こんな方におすすめ
お顔の肌荒れが気になる方・フェイスラインをすっきり見せたい方
ミント系のさわやかな香りが好みの方。 シートマスク「玄武」
・こんな方におすすめ
エイジングケアをしたい方・お顔の乾燥が気になる方
柑橘系の香りがお好きな方
上記よりお好きなシートマスクをお一人様1枚お選びいただけます。 ※THE JUNEI HOTEL京都御所西のご宿泊限定プランでございます。 -

2026.9.04 お知らせ
サウナメディアSISUに紹介されました
京都のホテル・旅館のサウナを紹介する記事にて、THE JUNEI HOTELをご紹介いただきました。
京都のホテルや旅館で味わう特別なサウナ14選|サウナメディアSISU -
2026.9.04 お知らせ
「京都観光旅行ガイド」にご紹介いただきました
京都の高級・老舗旅館を紹介する記事にて、THE JUNEI HOTEL 京都/京都 御所西をご紹介いただきました。
京都の旅館【高級&老舗12選】高級旅館を4つのタイプに分類|京都観光旅行ガイド -

2026.1.18 お知らせ
THE JUNEI HOTEL京都御所西でのご利用のみ 新プラン【心ほどけるルームアフタヌーンティープラン】のお知らせ
京都御所のほとりに静かに寄り添うTHE JUNEI HOTEL 京都御所西。
しっとり落ち着いた別邸の空間で、時間の流れがゆるやかにほどけていく午後。
客室にいながら京都の菓子文化と上質な創作イタリアンを一度に味わえる、特別なルーム・アフタヌーンティ、のど越し豊かな紅茶をお供にプライベートな空間で誰にも邪魔されない上質なひとときをゆっくりとご堪能くださいませ。
アフタヌーンティーメニュー(一例:季節により変わります)
【和菓子四種】
京菓子の伝統と四季を表現する「KAHOU」より、和の趣あふれる季節菓
【セイボリー三種】
割烹の技法を取り入れた「リストランテ野呂」からは、イタリアンの枠を超えた繊細なセイボリー
【紅茶】
オーガニックで良質な茶葉を提供する「T-branch」より人気のアールグレイ
客室というプライベートな空間で、誰にも邪魔されない上質なひとときをゆっくりとお過ごしください。
THE JUNEI HOTELならではの“静寂と美”を感じる、特別な午後を。 -

2025.10.08 お知らせ
「THE JUNEI HOTEL 京都」「コンデナスト・トラベラー2025年 リーダーズ・チョイス・アワード2025」において、「日本のトップ...
「THE JUNEI HOTEL 京都 」は、2025年10月7日に米国旅行誌『コンデナスト・トラベラー(Condé Nast Traveler)』が発表した、旅の読者投票において最も歴史があり、権威のある「コンデナスト・トラベラー 2025 リーダーズ・チョイス・アワード(Condé Nast Traveler 2025 Readers’ Choice Awards)」を受賞しました。当ホテルは2020年の開業以来初、「日本のトップホテル」部門で、第5位に選定されました。
表彰リンク:https://www.cntraveler.com/gallery/top-hotels-in-japan
世界各国の旅慣れた旅行者からの投票による世界的に権威のある日本のホテルランキングにおいて、第5位に選出していただけたことを大変光栄に思っております。これもひとえに 2020年3月28日に開業以来、ご宿泊頂きましたお客様、及びご協力下さいました関係者の方々の温かいご支援のお蔭であり、皆さまの支えに心から感謝申し上げます。 「JUNEI」とは「壽寧」と書きます。丁寧におもてなしをお届けし、お客様の壽(ことぶき)にそっと寄り添い、壽を届けたいという想いが込められています。 今後も、一人一人のお客様の壽を心からお祈りし、お心に丁寧に寄り添わせていただくホテルとなりますよう、従業員一同、より一層業務に精励致す所存でございます。 ホテルという枠にとどまらず、日本・京都の奥深さ、素晴らしさをお客様に感じて頂き、ご滞在中の時間が一生忘れられない輝きとなってお客様の記憶に残ることを願っております。 -

2025.8.09 お知らせ
清涼感溢れる夏のお菓子・果氷をご提供中です
平素よりTHE JUNEI HOTEL京都御所西をご愛顧いただき誠にありがとうございます。
本年7月にて開業9年目を迎えた当ホテルは京の街並みに佇む宿として僭越ながら歴史を刻みつつ引き続き邁進して参る所存でございます。
酷暑に見舞われております本年の京都において、涼をとる一助になるようご滞在いただくお客様へ菓匠・KAHOU様の見た目にも艶やかなアイスバー・果氷(かおり)をご提供しております。
3種(ベリー・オレンジ・抹茶)の中からお好きな味を選んでいただけ、葛を含んだ果氷は通常のアイスバーよりももっちりと食べ応えもありながらアイスならではのひんやりとした食感で夏の暑さを和らげる一品でございます、昨年も同品をご提供致しましたが大変ご好評のお声をいただき本年も継続する形をとらせていただきました。
チェックインの際にご案内しておりますのでこの機会にぜひお召し上がりくださいませ。
THE JUNEI HOTEL京都御所西
-

2024.12.21 お知らせ
【JUNEI Memory〜柚子湯で至極のバスタイムを】
平素よりTHE JUNEI HOTEL京都御所西をご愛顧賜り誠にありがとうございます。
本日、12月21日チェックインから2月3日チェックイン期間において下記イベントを開催し特典を全てのお部屋へ提供致します。
冬のご滞在を特別なものへ彩る催しをご用意致しました。
銭湯が誕生した江戸時代に遡り始まった日本古来の習わしである柚子風呂。
1年のうちで太陽の位置が最も低く、日照時間が最も短くなる日を冬至としそれを境に太陽の力が甦り「陰」が極まり「陽」に転じる、全てが「好運」へ向かうという意味の「一陽来復」を意味する柚子湯で冬の寒さを和らげ身をほぐしながら至福の入浴をお楽しみいただきたいと願いを込めて。
爽やかで芳醇な柚子の香がバスタイムを至福の時間へと染め上げます。
ぜひお試しくださいませ。
【イベント内容】
柚子果実を各お部屋バスルームへご用意
【イベント期間】
2024年12月21日(冬至)から2025年2月3日まで
皆様のご来館を心よりお待ちしております。
THE JUNEI HOTEL京都御所西 -

2024.7.01 お知らせ
THE JUNEI HOTEL京都御所西開業8年目のお知らせ
平素よりTHE JUNEI HOTEL京都御所西をご愛顧いただきありがとうございます。
皆さまのお陰をもって7月1日に当館は開業8年目を無事に向えることができました。
7月は新たな季節の催し「JUNEI Memory〜喉を潤す氷菓子と
真夏の夜を思い出深く彩るからかさ」を開催しております。
皆さまに寄り添ったおもてなしが叶う宿になり得ますようこれからも精励してゆく所存でございます。
皆さまのご来館を心よりお待ち申し上げております。
THE JUNEI HOTEL京都御所西
ARCHIVE


 空室検索
ベストレート保証 公式サイトからのご予約が最もお得です
